No Image

USN-4586-1: PHP ImageMagick vulnerability

2020-10-20 KENNETH 0

USN-4586-1: PHP ImageMagick vulnerability It was discovered that PHP ImageMagick extension didn’t check the address used by an array. An attacker could use this issue to cause PHP ImageMagick to crash, resulting in a denial of service. Source: USN-4586-1: PHP ImageMagick vulnerability

No Image

USN-4593-1: FreeType vulnerability

2020-10-20 KENNETH 0

USN-4593-1: FreeType vulnerability Sergei Glazunov discovered that FreeType did not correctly handle certain malformed font files. If a user were tricked into using a specially crafted font file, a remote attacker could cause FreeType to crash or possibly execute arbitrary code with user privileges. Source: USN-4593-1: FreeType vulnerability

No Image

USN-4592-1: Linux kernel vulnerabilities

2020-10-20 KENNETH 0

USN-4592-1: Linux kernel vulnerabilities Andy Nguyen discovered that the Bluetooth L2CAP implementation in the Linux kernel contained a type-confusion error. A physically proximate remote attacker could use this to cause a denial of service (system crash) or possibly execute arbitrary code. (CVE-2020-12351) Andy Nguyen discovered that the Bluetooth A2MP implementation in the Linux kernel did not properly initialize memory in some situations. A physically proximate remote attacker could use this to expose sensitive information (kernel memory). (CVE-2020-12352) Andy Nguyen discovered that the Bluetooth HCI event packet parser in the Linux kernel did not properly handle event advertisements of certain sizes, leading to a heap-based buffer overflow. A physically proximate remote attacker could use this to cause a denial of service (system crash) or possibly execute arbitrary code. (CVE-2020-24490) Source: USN-4592-1: Linux kernel vulnerabilities

No Image

USN-4591-1: Linux kernel vulnerabilities

2020-10-20 KENNETH 0

USN-4591-1: Linux kernel vulnerabilities Andy Nguyen discovered that the Bluetooth L2CAP implementation in the Linux kernel contained a type-confusion error. A physically proximate remote attacker could use this to cause a denial of service (system crash) or possibly execute arbitrary code. (CVE-2020-12351) Andy Nguyen discovered that the Bluetooth A2MP implementation in the Linux kernel did not properly initialize memory in some situations. A physically proximate remote attacker could use this to expose sensitive information (kernel memory). (CVE-2020-12352) Source: USN-4591-1: Linux kernel vulnerabilities

What Customers Tell Us They Need for Modern API Management

2020-10-20 KENNETH 0

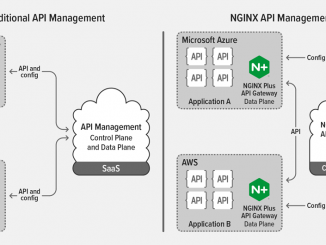
What Customers Tell Us They Need for Modern API Management As a Sales lead for NGINX at F5, I often interact with customers that are using more than one API management framework. One customer I spoke with has five at last count! Why is this? There can be many reasons, but one situation we come across again and again is that as customers are transforming their applications from monolithic architectures to more microservices‑based architectures, they’re finding that their traditional API management framework no longer satisfies all their requirements. Before we examine the ways these traditional frameworks are no longer adequate, let’s take a look back at how we got to where we are today… The Evolution of Software Integration Architecture During the early 2000s we saw a growing requirement for an integration layer able to connect various front‑end services to [ more… ]