No Image

USN-4542-1: MiniUPnPd vulnerabilities

2020-09-26 KENNETH 0

USN-4542-1: MiniUPnPd vulnerabilities It was discovered that MiniUPnPd did not properly validate callback addresses. A remote attacker could possibly use this issue to expose sensitive information. (CVE-2019-12107) It was discovered that MiniUPnPd incorrectly handled unpopulated user XML input. An attacker could possibly use this issue to cause MiniUPnPd to crash, resulting in a denial of service. (CVE-2019-12108, CVE-2019-12109) It was discovered that MiniUPnPd incorrectly handled an empty description when port mapping. An attacker could possibly use this issue to cause MiniUPnPd to crash, resulting in a denial of service. (CVE-2019-12110) It was discovered that MiniUPnPd did not properly parse certain PCP requests. An attacker could possibly use this issue to cause MiniUPnPd to crash, resulting in a denial of service. (CVE-2019-12111) Source: USN-4542-1: MiniUPnPd vulnerabilities
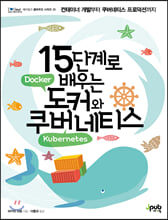
[도서] 15단계로 배우는 도커와 쿠버네티스

2020-09-25 KENNETH 0

[도서] 15단계로 배우는 도커와 쿠버네티스 분야별 신상품 – 국내도서 – 컴퓨터와 인터넷 [도서]15단계로 배우는 도커와 쿠버네티스 타카라 마호 저/이동규 역 | 제이펍 | 2020년 10월 판매가 30,600원 (10%할인) | YES포인트 1,700원(5%지급) 한 권으로 배우는 도커와 쿠버네티스 실전 가이드! 컨테이너 기술에 처음 입문하는 독자도 체계적으로 실력을 쌓아갈 수 있도록 도커부터 시작하여 쿠버네티스의 전반적인 기능을 기초부터 단계별로 학습할 수 있 Source: [도서] 15단계로 배우는 도커와 쿠버네티스

No Image

USN-4540-1: atftpd vulnerabilities

2020-09-25 KENNETH 0

USN-4540-1: atftpd vulnerabilities Denis Andzakovic discovered that atftpd incorrectly handled certain malformed packets. A remote attacker could send a specially crafted packet to cause atftpd to crash, resulting in a denial of service. (CVE-2019-11365) Denis Andzakovic discovered that atftpd did not properly lock the thread list mutex. An attacker could send a large number of tftpd packets simultaneously when running atftpd in daemon mode to cause atftpd to crash, resulting in a denial of service. (CVE-2019-11366) Source: USN-4540-1: atftpd vulnerabilities

No Image

USN-4539-1: AWL vulnerability

2020-09-25 KENNETH 0

USN-4539-1: AWL vulnerability Andrew Bartlett discovered that DAViCal Andrew’s Web Libraries (AWL) did not properly manage session keys. An attacker could possibly use this issue to impersonate a session. (CVE-2020-11728) Source: USN-4539-1: AWL vulnerability

No Image

USN-4536-1: SPIP vulnerabilities

2020-09-25 KENNETH 0

USN-4536-1: SPIP vulnerabilities Youssouf Boulouiz discovered that SPIP incorrectly handled login error messages. A remote attacker could potentially exploit this to conduct cross-site scripting (XSS) attacks. (CVE-2019-16392) Gilles Vincent discovered that SPIP incorrectly handled password reset requests. A remote attacker could possibly use this issue to cause SPIP to enumerate registered users. (CVE-2019-16394) Guillaume Fahrner discovered that SPIP did not properly sanitize input. A remote authenticated attacker could possibly use this issue to execute arbitrary code on the host server. (CVE-2019-11071) Sylvain Lefevre discovered that SPIP incorrectly handled user authorization. A remote attacker could possibly use this issue to modify and publish content and modify the database. (CVE-2019-16391) It was discovered that SPIP did not properly sanitize input. A remote attacker could, through cross-site scripting (XSS) and PHP injection, exploit this to inject arbitrary web script or HTML. (CVE-2017-15736) Alexis [ more… ]